Phishing Email and SMS Safety: Spot Fake Links Before You Click
Understand how phishing messages create urgency and use a simple process to inspect links, attachments and account alerts safely.
Phishing messages imitate banks, delivery companies, employers and government services. Their purpose is to make you click a link, open an attachment or reveal a password. A calm verification process can prevent many attacks.
Look for urgency and fear
Messages claiming that an account will close today, a parcel is held or a refund will expire are designed to stop careful thinking. Pause and verify through the official app or website instead of using the message link.
Inspect the sender and destination
Check the complete email address and the spelling of the domain. On a computer, hover over a link; on a phone, press and hold only when you understand the preview. Misspellings, shortened URLs and unrelated domains need caution.
Do not share authentication codes
Banks and legitimate services do not need your OTP, UPI PIN or password through a chat or phone call. If someone asks you to read a code aloud, end the conversation and contact the organisation independently.
Handle attachments carefully
Unexpected documents or APK files may install malware. Do not enable macros or install apps from message links. Keep security updates active and scan files when appropriate.
If you clicked a suspicious link
Close the page, do not enter information and update the affected password using the official site. Check account activity, enable multi-factor authentication and report the message to the relevant provider.
Final takeaway
Do not let a message choose your next action. Verify alerts independently, protect authentication details and treat unexpected links and attachments as untrusted until proven safe.
Phishing Targets Emotion Before Technology
Most phishing messages try to create urgency, fear, curiosity or greed. They may claim that an account will close, a parcel is held, a refund is waiting or a boss needs an immediate transfer. The safest first response is to slow down. A legitimate issue can usually be checked through the organisation’s official app, bookmarked website or published phone number.
Read the Sender and Link Separately
A display name such as “Your Bank” can be changed easily. Inspect the complete email address. On a computer, hover over a link; on a phone, press and hold without opening it to preview the destination. Look for misspellings, extra words, unusual subdomains and shortened links. HTTPS only means the connection is encrypted—it does not prove the site is honest.
Common Warning Signs
- An unexpected attachment, QR code or login request
- Threats of arrest, account closure or immediate financial loss
- A request for password, OTP, UPI PIN or remote access
- Payment by gift card, cryptocurrency or an unfamiliar UPI ID
- A colleague or relative suddenly using a new number
- Grammar, branding or domain details that do not match
Example: A Fake KYC Message
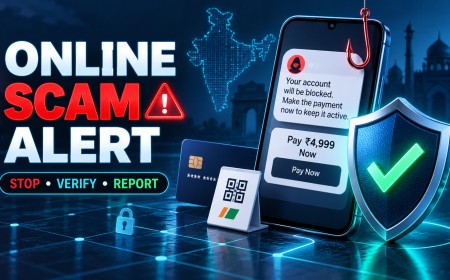
An SMS says your bank account will be blocked tonight and includes a link to “update KYC.” Do not use the link or call the listed number. Open the bank’s official app or type its known website yourself. If there is no alert inside your account, contact the bank through the number printed on your card or its verified website.
What to Do After Clicking
If you clicked but entered nothing, close the page, avoid downloading files and run updated security checks. If you entered a password, change it immediately from a trusted device and sign out of other sessions. Enable multi-factor authentication, review recovery details and check for unauthorised transactions. If banking information or money is involved, contact the bank immediately.
Reporting in India
For suspected financial cyber fraud, call 1930 promptly and submit details at the National Cyber Crime Reporting Portal. Preserve the original message, URL, sender details, transaction ID and screenshots. Do not forward a malicious link to friends as a warning; share a screenshot with the dangerous URL obscured.
Protect Your Accounts Before an Attack
- Use unique passwords and a reputable password manager.
- Turn on multi-factor authentication where available.
- Keep operating systems, browsers and apps updated.
- Review account activity and recovery options regularly.
- Restrict installation of apps from unknown sources.
Official Guidance
CERT-In’s online-scam advisory recommends avoiding links or attachments from unknown senders, typing an organisation’s URL directly and never sharing sensitive information under pressure. These habits are useful even when a message looks professionally designed.
Protect Family Members from Repeat Scams
Create a household rule: no urgent transfer is made until the requester is called on a previously saved number. Help older relatives bookmark bank websites and save official support numbers. Discuss scams without blaming victims; shame can delay reporting and give criminals more time.
Frequently Asked Questions
Can a QR code be phishing? Yes; it can hide a malicious destination, so verify its source. Does multi-factor authentication stop every attack? No, but it adds valuable protection; never approve an unexpected prompt. Should I reply “STOP” to a suspicious SMS? Replying can confirm the number is active. Use your device or telecom provider’s reporting tools instead.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Software developer with expertise in full-stack web development and financial market analysis, specializing in building tracking tools for trading metrics.
Comments (0)