Domain, DNS, SSL and CDN: A Beginner’s Guide for Website Owners
Understand how domains, DNS records, SSL certificates and CDNs work together, with safe setup steps and a practical troubleshooting checklist.
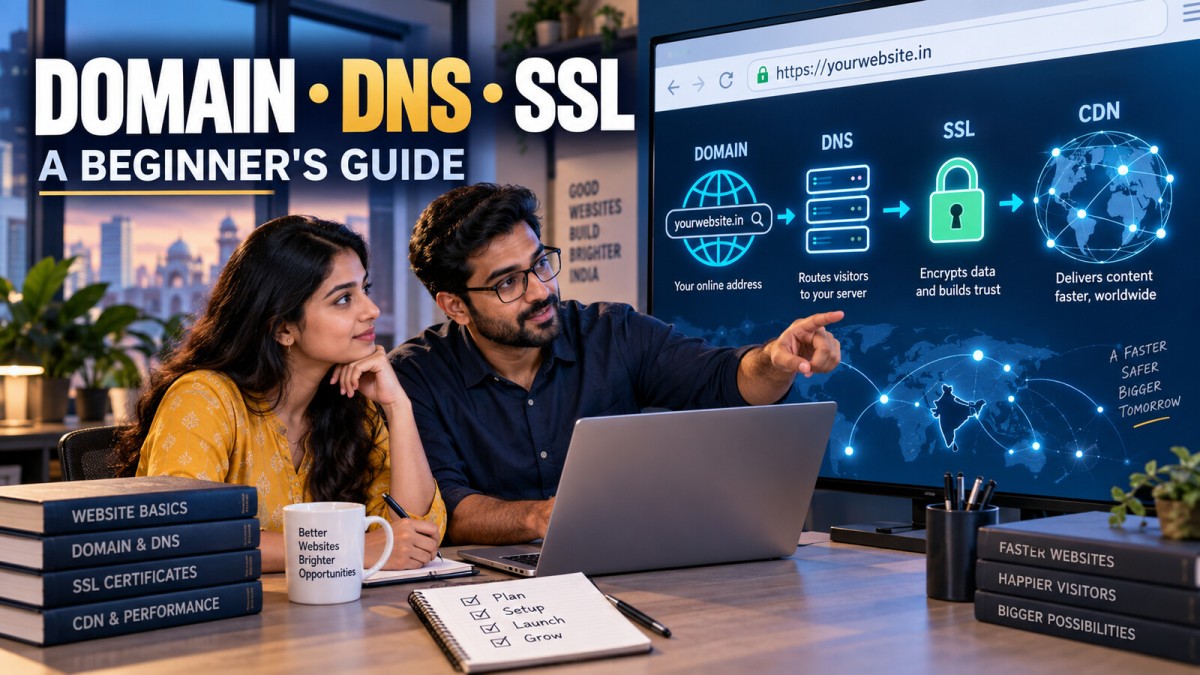
A website can fail even when its hosting server is healthy. The domain, DNS records, SSL certificate and CDN each perform a different job, and a problem in one layer can make the entire site appear offline. Understanding these basics helps website owners communicate with developers and avoid risky changes.
Domain Name: The Human-Friendly Address
A domain is the address people type, such as example.in. Registration gives the holder the right to use that name for a defined period; it does not permanently purchase the name. Keep registrant details current, enable account security and renew early.
DNS: The Internet’s Routing System
DNS records tell browsers and services where to find the website, email and verification endpoints. Nameservers identify the DNS provider. An A record points to an IPv4 address, AAAA points to IPv6, CNAME aliases one hostname to another, MX directs email and TXT records often support verification and email security.
Why DNS Changes Take Time
Resolvers cache records for a period controlled partly by time-to-live values. After a change, different users may temporarily receive different answers. Lowering TTL before a planned migration can help, but it does not make every cache update instantly.
SSL and HTTPS
An SSL/TLS certificate helps encrypt traffic between a visitor’s browser and the website and confirms control of the requested hostname. Modern browsers show HTTPS, but the padlock does not prove that a business itself is trustworthy. Certificates expire and should renew automatically with monitoring.
Common Certificate Problems
Typical problems include an expired certificate, missing hostname, incomplete certificate chain, incorrect server time or mixed content loaded over HTTP. Test both the main domain and www version, and verify redirects after renewal or migration.
CDN: Content Closer to Visitors
A content delivery network can cache static assets at locations closer to users, reduce load on the origin server and absorb some traffic spikes. A CDN does not fix slow database queries or poor application code. Cache rules must also protect private pages and frequently changing content.
Safe Setup Order
- Confirm domain ownership and registrar access.
- Record the current nameservers and DNS zone.
- Configure the hosting origin and test it privately.
- Add required DNS records.
- Issue and verify the certificate.
- Enable redirects to HTTPS.
- Add CDN caching carefully and test forms and logins.
Email Protection During DNS Changes
Do not replace a DNS zone without copying MX and important TXT records. Missing email records can interrupt delivery even when the website loads. Document SPF, DKIM and DMARC settings and coordinate changes with the email provider.
Security Basics
Use strong authentication and recovery controls at the registrar and DNS provider. Limit account access, review API keys and enable registry lock where appropriate. An attacker who controls DNS can redirect visitors even without accessing the web server.
Troubleshooting Checklist
- Check domain expiry and nameservers.
- Compare DNS answers from more than one resolver.
- Confirm the origin server responds.
- Inspect certificate hostname and expiry.
- Temporarily bypass CDN caching when isolating an origin problem.
- Review recent changes before modifying more records.
Document Everything
Maintain a simple inventory containing registrar, DNS provider, hosting provider, certificate method, CDN account, renewal dates and responsible contacts. Store credentials in a password manager, not in the inventory itself.
Editorial note: DNS and security configurations vary by provider. Take a verified backup of existing records and use qualified technical support when changing production systems.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Software developer with expertise in full-stack web development and financial market analysis, specializing in building tracking tools for trading metrics.
Comments (0)